SYSTEM TIME: 00:00:00
SECURITY: ENCRYPTED
★
CYBER
INTELLIGENCE
TOP SECRET

INTELLIGENCE AGENCY

OFFICE OF THE DIRECTOR | PERSONNEL RECORDS DIVISION

FILE REF: CIA-772-B-991

OPERATIONAL SUMMARY

Currently embedded at Georgia Tech’s COEUS/Astrolavos Lab, with additional field experience in cyber threat intelligence and cyber risk consulting, I am a cybersecurity researcher focused on malware analysis, threat intelligence, software supply chain security, and AI security and safety.

I’m interested in understanding how systems get compromised, building tools that make defense faster and more effective, and automating the boring stuff. My work spans malware reverse engineering, binary analysis, threat intelligence, and security automation. I’m particularly interested in using AI to augment security research and analysis, while also understanding the security risks posed by AI systems themselves.

BADGES

PROGRAMMING
Python
Python
C
C
C++
C++
Bash
Bash
CLOUD & INFRA
AWS
AWS
Docker
Docker
Kubernetes
Kubernetes
Linux
Linux
Git
Git
SECURITY & REVERSE ENGINEERING
IDA Pro
Ghidra
x64dbg
YARA
Wireshark
Suricata
VirusTotal
Recorded Future
AI SECURITY
LLM Security
Model Red Teaming
Adversarial ML
Prompt Engineering
RAG
MCP
ACADEMIC CREDENTIALS

TRAINING RECORD
M.S. COMPUTER ENGINEERING — Georgia Institute of Technology · January 2025–December 2026 (anticipated)
B.S. COMPUTER ENGINEERING — Georgia Institute of Technology · August 2020–December 2024

FIELD ASSIGNMENTS

GRADUATE RESEARCH ASSISTANT — COEUS/ASTROLAVOS LAB, GEORGIA TECHACTIVE
JANUARY 2026 – AUGUST 2026 · ATLANTA, GA
    SOFTWARE SUPPLY CHAIN SECURITY:
  • Recreated and validated 3 research-grade binary analysis techniques for library decomposition and source-boundary recovery by rebuilding environments with Docker and reproducing published evaluation results.
  • Implemented missing metric-generation Python scripts for accuracy, precision, recall, and F1 scores, and evaluated reproduced research artifacts on a custom Linux application dataset.
  • MALWARE CLASSIFICATION:
  • Developed an AI-assisted malware analysis pipeline by integrating LLM APIs for semantic feature extraction and malware family relationship discovery, combined with DIE-based packer detection to improve behavioral feature analysis.
  • Debugged a critical filtering flaw that caused 74% of same-family malware sample pairs to be incorrectly classified as unrelated by analyzing 166 sample pairs across 27 families and developing a 6-category root cause taxonomy.
CYBER RISK ANALYST (CONSULTING) — PRAMUKH TRANSPORT LTD.CLOSED
AUGUST 2022 – JANUARY 2025 · KENYA · PART-TIME
  • Conducted a red-team tabletop exercise and threat model across 3 attack objectives, identifying exposed RDP and weak credential management as top risks to transport operations and driving MFA adoption to strengthen access controls.
IT TECHNICIAN INTERN — AKSHAR AUTO SPARE HOUSECLOSED
JUNE 2020 – AUGUST 2020 · KENYA
  • Hardened 7 workstations through OS patching, vulnerability scanning, and password policy enforcement.

CASE FILES

AGENTIC AI SYSTEM FOR MALWARE BEHAVIOR DISCOVERYFILE 309
AGENTIC AI SYSTEM FOR MALWARE BEHAVIOR DISCOVERY thumbnail

OBJECTIVE: Auto-locate anti-analysis triggers in malware and generate sandbox-environment patches to defeat them.

TECH STACK: Python, LLM-agent orchestration, static disassembly + dynamic API-call analysis

IMPACT: Uncovered 22 new malware behaviors on a class leaderboard, tied for the most of any submission, at $0.034 LLM cost.

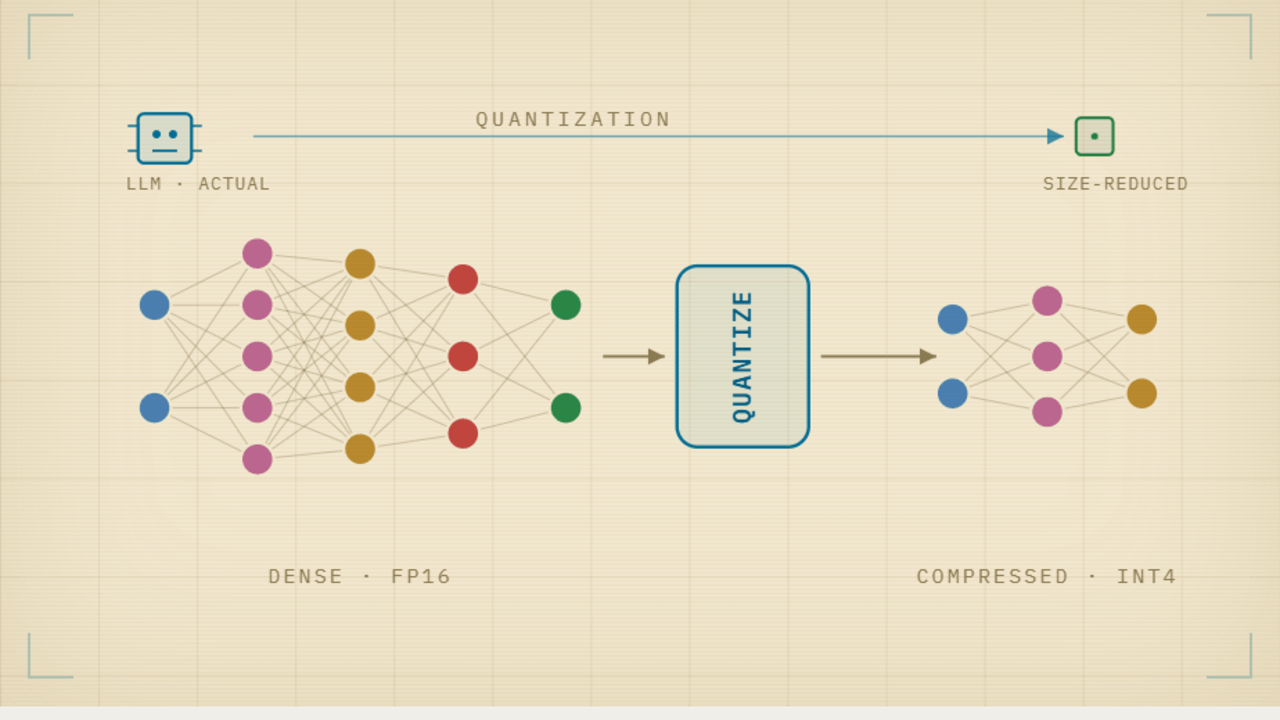
LLM SAFETY UNDER QUANTIZATIONFILE 506
LLM SAFETY UNDER QUANTIZATION thumbnail

OBJECTIVE: Quantify whether compressing an LLM for local deployment weakens its jailbreak guardrails (team of 4).

TECH STACK: Python, HuggingFace Transformers, BitsAndBytes, llama.cpp/GGUF, JailbreakBench

IMPACT: Quantization method mattered more than compression level; model choice mattered most of all.

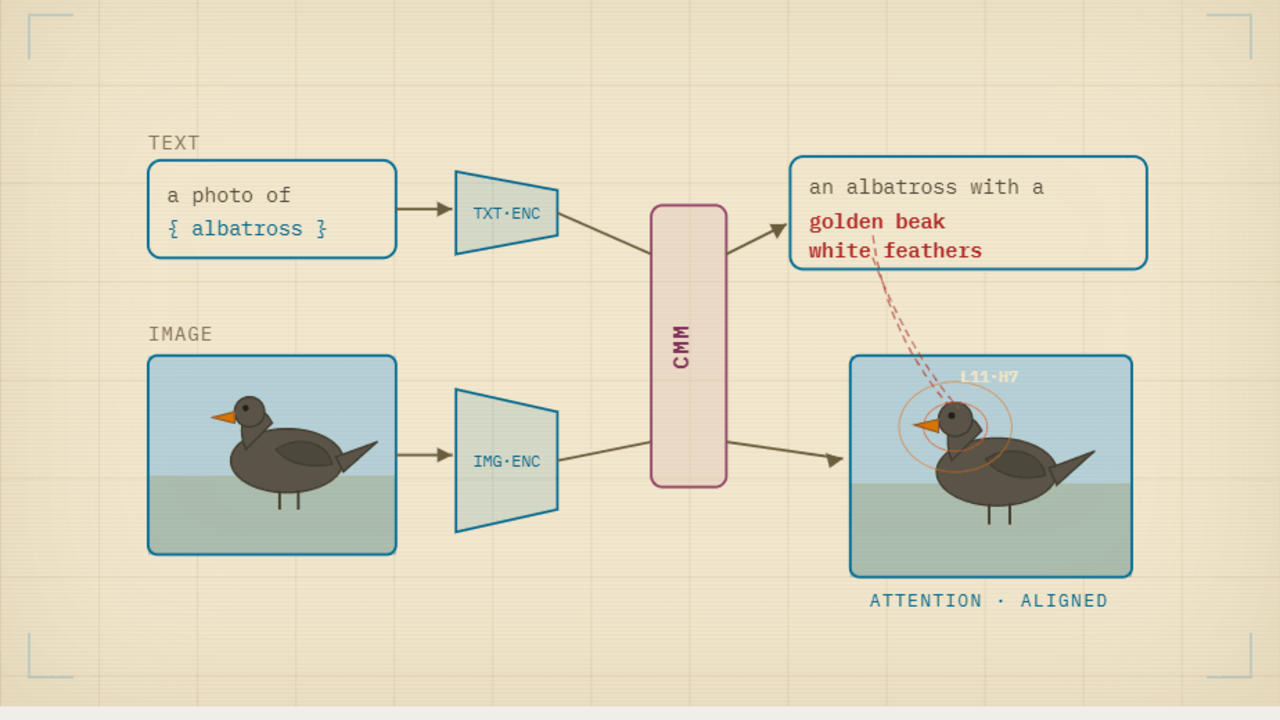
VLM ATTENTIONFILE 207
VLM ATTENTION thumbnail

OBJECTIVE: Determine when VLMs genuinely use visual evidence vs. linguistic priors, across dialogue turns (team of 4).

TECH STACK: Python, BLIP-2, LLaVA-1.5, Qwen2.5-VL, attention rollout, COCO dataset

IMPACT: Qwen2.5-VL was the most visually grounded of the three models tested; BLIP-2 the least.

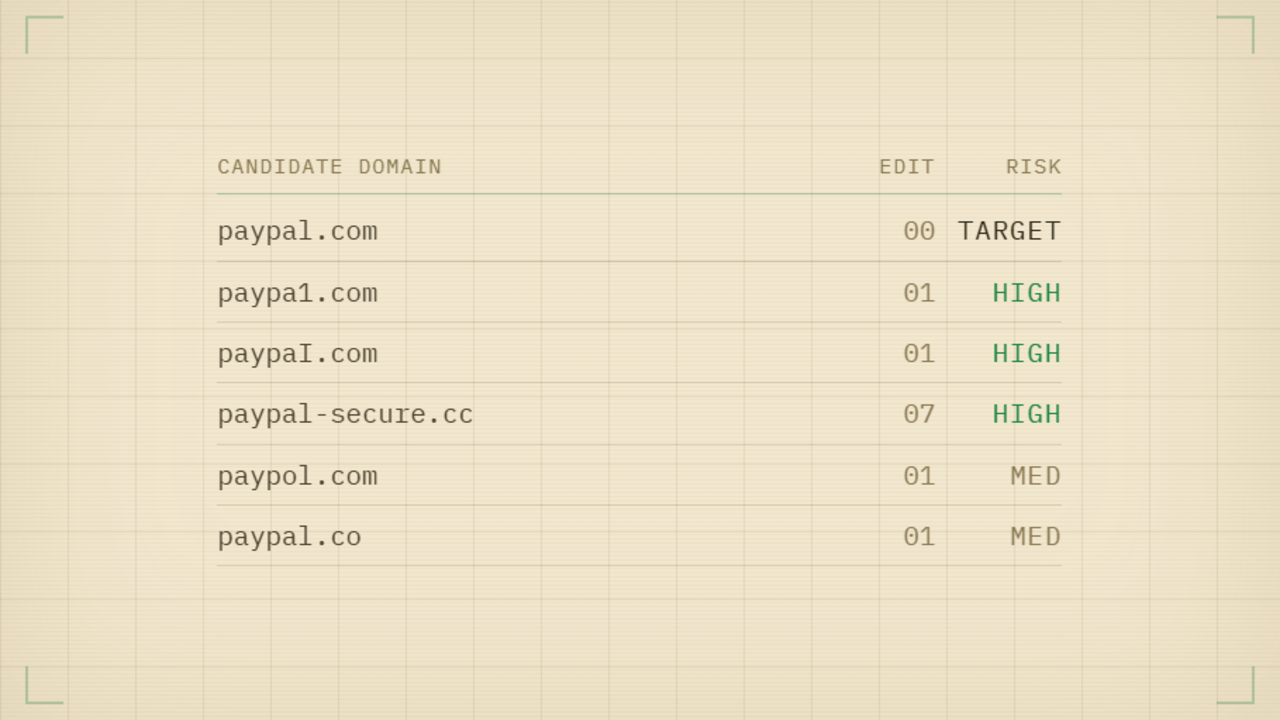
DEFENSIVE DOMAIN REGISTRATIONSFILE 099
DEFENSIVE DOMAIN REGISTRATIONS thumbnail

OBJECTIVE: Decide which typo-squatted domains a brand should pre-register when the budget covers only a fraction of them (team of 4).

TECH STACK: Python, hashcat rule syntax, Damerau-Levenshtein edit distance, NumPy, Jupyter

IMPACT: Mined 591 real domain disputes into a ranked grammar of squatting patterns; the resulting strategy was selected over the competing proposal.

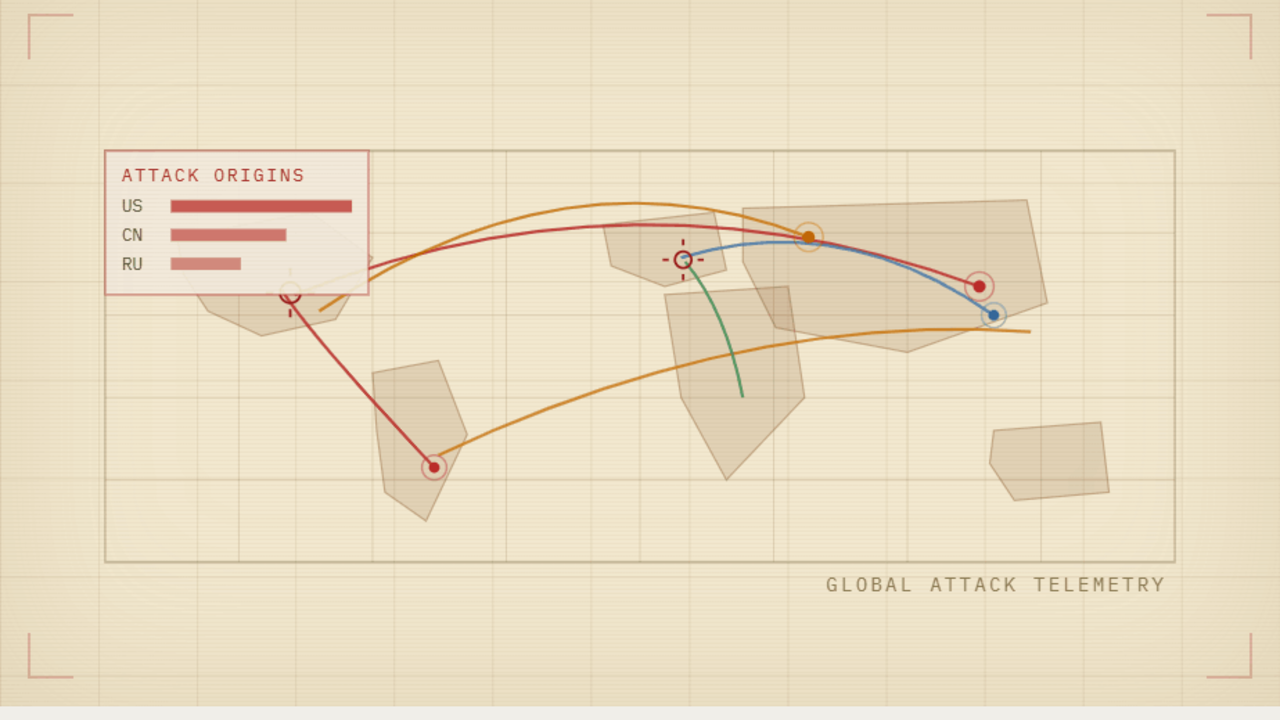
DATA ANALYTICS - DRIVERS FOR CYBER CONFLICTFILE 655
DATA ANALYTICS - DRIVERS FOR CYBER CONFLICT thumbnail

OBJECTIVE: Identify the real structural drivers of state-sponsored cyberattack targeting frequency (solo project).

TECH STACK: R, OLS regression, CFR Cyber Operations Tracker, V-Dem, World Bank Open Data

IMPACT: Internet penetration — not regime type — is the dominant predictor of targeting (p<0.01).

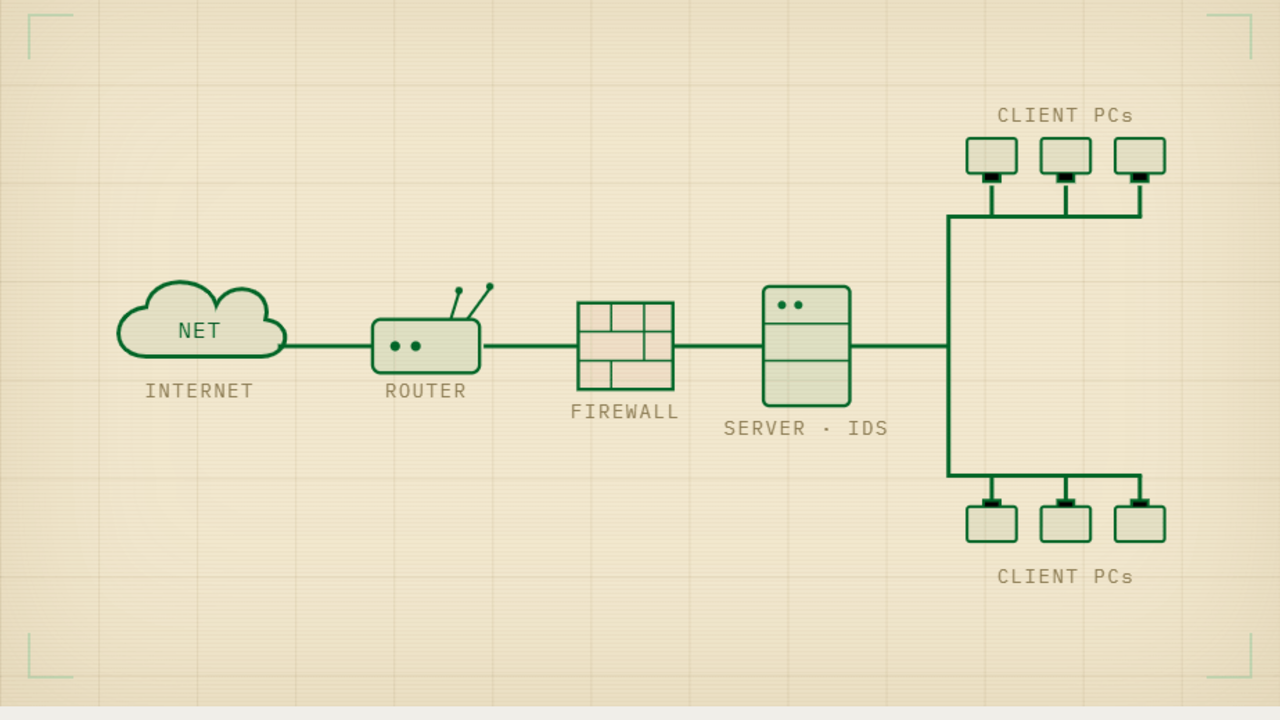
ML-BASED IDSFILE 711
ML-BASED IDS thumbnail

OBJECTIVE: Remove backdoor poisoning from a deep-learning IDS via machine unlearning, cross-verified by a rule-based IDS (team of 3).

TECH STACK: Python, PyTorch, Suricata, CIC-IDS2017

IMPACT: Restored 100% detection of backdoored flows post-unlearning with clean accuracy unchanged at 99.27%.

SECURE CLOUD WEB APPLICATIONFILE 824
SECURE CLOUD WEB APPLICATION thumbnail

OBJECTIVE: Zero-trust cloud web application with hardened authentication and full audit logging.

TECH STACK: Node.js, React, AWS, Terraform, OAuth2

IMPACT: Passed external penetration test with zero critical findings.

ANDROID GAME DEVELOPMENTFILE 512
ANDROID GAME DEVELOPMENT thumbnail

OBJECTIVE: Apply core OOP design patterns to build a complete, testable Android game (team of 7).

TECH STACK: Java, Android SDK, Gradle, JUnit 4

IMPACT: Built the combat system, the enemy Factory (skeleton and vampire), Strategy-pattern movement across all three maps, and the core game screens.

CONTACT

Transmit through one of the verified contact channels below:

To view the full history of field missions and technical training, download the primary personnel file:

DOWNLOAD RESUME.PDF

WARNING: UNAUTHORIZED ACCESS IS A FEDERAL OFFENSE UNDER THE ESPIONAGE ACT.